

- One auditor running both engagements in parallel
- One comprehensive audit report
- Quarterly testing of agents against real-world risks
Joint audit process
Both frameworks are scoped upfront and pursued in the same audit window, in one engagement with your organization’s existing SOC 2® auditor. This helps organizations to cover agents & cybersecurity in one engagement.Scoping
Each framework is scoped to its relevant domain. SOC 2® covers the organizational systems within its audit scope. AIUC-1 covers the specified agents or platforms and their security, safety and reliability risks.
Read more: SOC 2® coverage
Read more: SOC 2® coverage
- Scope defined in the Management Assertion
- Covers security and data controls across the whole organization: access, encryption, change management, incident response
- Mix of technical and governance controls
Read more: AIUC-1 coverage
Read more: AIUC-1 coverage
- Scope defined in the Management Assertion - limited to AI agent systems
- Covers agent-specific security, safety and reliability risks
- Mix of technical & governance controls
- Includes quarterly technical evaluations of agents themselves
More on the testing methodology here.
Read more: Certifying individual agents vs. agent platforms
Read more: Certifying individual agents vs. agent platforms
AIUC-1 Certification is used by organizations in two ways: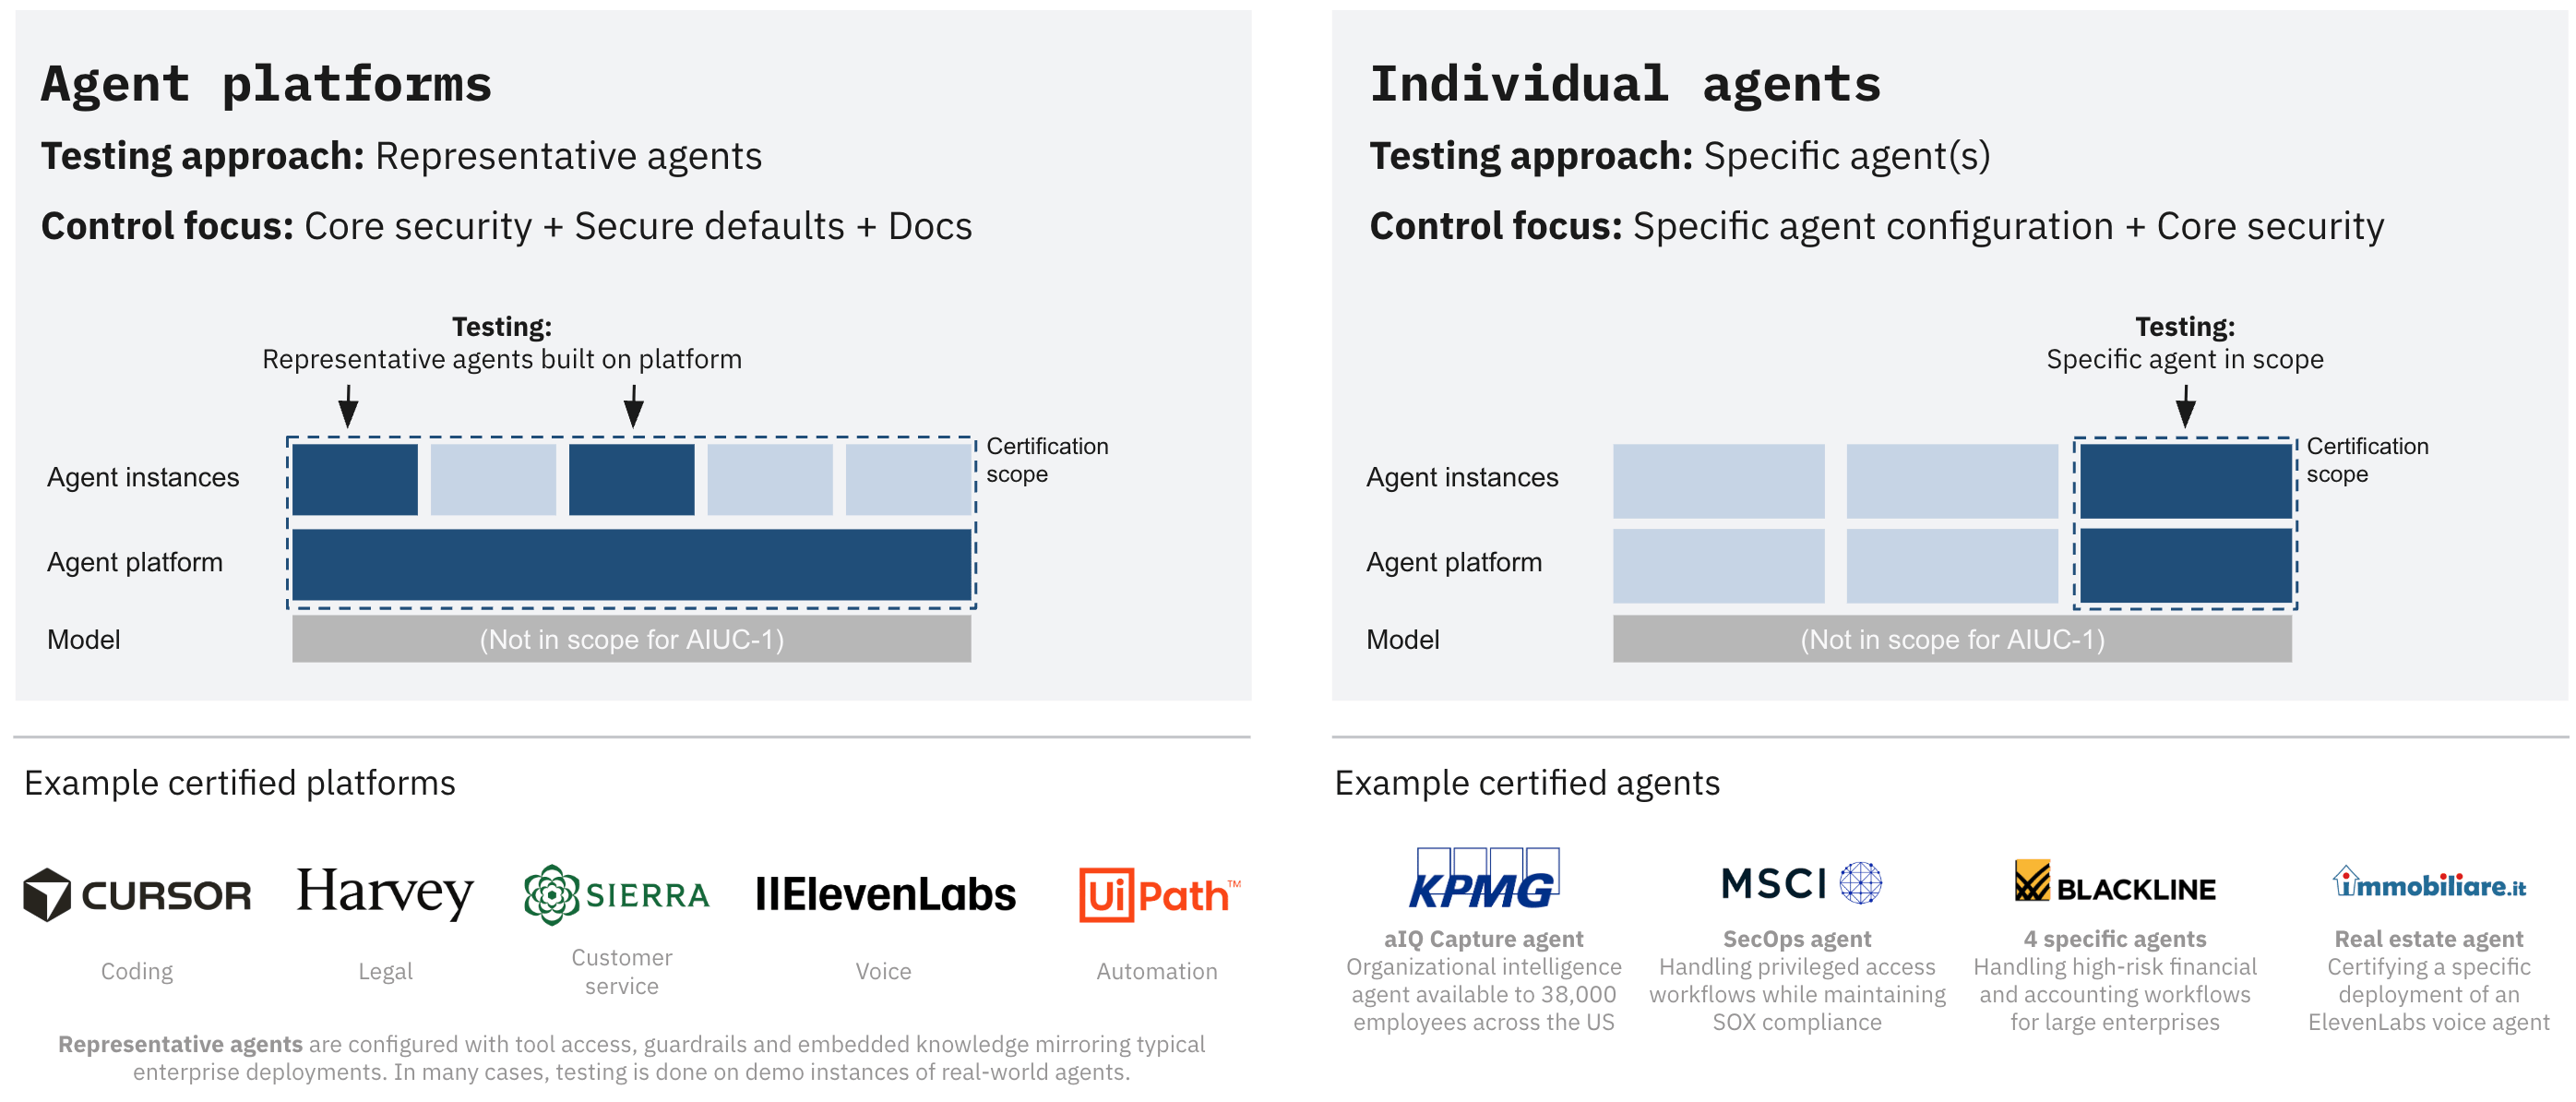
Evidence Collection
The joint engagement simplifies evidence collection for organizations:- Auditors typically share one combined request list
- Overlapping requests are only submitted once
- Organizations can use their desired GRC platform for the joint engagement
Final deliverable
After completing the full audit, organizations will receive one unified audit report combining:- Full SOC 2® attestation report covering Security and additional Trust Services Criteria as appropriate
- Full AIUC-1 certification report of applicable AIUC-1 requirements including technical evaluation results of agent behaviour.
FAQs
Which auditors offer SOC 2® & AIUC-1 together
Which auditors offer SOC 2® & AIUC-1 together
SOC 2® + AIUC-1 is available with BDO, Deloitte, EisnerAmper, EY, Grant Thornton, KPMG, PwC and Schellman. Additional firms hold provisional AIUC-1 accreditation - contact us here if you are interested in pursuing agent certification with another auditor.
When is SOC 2® & AIUC-1 relevant for organizations?
When is SOC 2® & AIUC-1 relevant for organizations?
SOC 2® + AIUC-1 is relevant for organizations:
- Developing agents & agent platforms sold to enterprises
- Deploying agents in high-risk environments - whether developed in-house or by vendors
- Subject to regulatory requirements for agents such as SOX, the EU AI Act, CA SB 243, NYC Local Law 144
- Using coding agents for production code (coding-agents are a typical AIUC-1 use case)
- Facing AI security reviews or questionnaires from enterprise buyers
When is SOC 2® & AIUC-1 not relevant for organizations?
When is SOC 2® & AIUC-1 not relevant for organizations?
SOC 2® + AIUC-1 is less relevant for organizations:
- Primarily using AI chatbots like Copilot, Claude or ChatGPT
- Using agents for low-risk use cases that are internally facing
- Restricting agents from accessing sensitive data and activate tools
- Not subject to new AI regulation
- Developing agents primarily sold to small companies with limited security requirements
What does this add to SOC 2® on its own?
What does this add to SOC 2® on its own?
The joint offering adds AI agent security to your SOC 2® audit through one combined engagement. AIUC-1 covers agent-specific security, safety and reliability risks and requires technical evaluations to validate agent deployments.
Who are all parties involved and the responsibilities of each?
Who are all parties involved and the responsibilities of each?
- Licensed CPA firms perform the SOC 2® & AIUC-1 engagement and issue the report.
- AIUC or accredited technical evaluation body runs the quarterly technical testing.